
In this Article
To use curl with proxy, use curl -x http://HOST:PORT https://example.com to select a proxy. Replace HOST and PORT with your provider’s endpoint, and add -U when proxy authentication is required.
A proxy routes the request through another server; the proxy scheme determines how curl connects to that server. Start with one request, verify the observed IP, then configure authentication, DNS and persistence. The official curl manual documents these options.
Key Facts
- Use -x to select a proxy for a curl request.
- -U supplies proxy credentials separately from destination authentication.
- curl ignores uppercase HTTP_PROXY.
- socks5h:// delegates destination hostname resolution to the proxy.
- An HTTPS proxy encrypts the connection between curl and the proxy.
- Our rotating sample returned 10 distinct exit IPs across 10 requests.
- Our sticky sample returned one exit IP across 10 requests.
Curl with proxy: quick-start commands
Select the proxy with -x and keep the destination URL separate. These commands succeeded in our quick run on October 20, 2026; USER and PASS are replacement markers, not working credentials.
HTTP proxy with separate authentication:
curl -x http://gw.dataimpulse.com:823 --proxy-user USER:PASS https://api.ipify.orgHTTPS connection to the proxy:
curl -x https://gw.dataimpulse.com:823 -U USER:PASS https://api.ipify.orgSOCKS5 with destination DNS handled by the proxy:
curl -x socks5h://USER:[email protected]:824 https://api.ipify.orgEach returned HTTP 200 and a residential exit IP rather than our server’s IP. In this run, the HTTPS proxy connection on port 823 presented a valid certificate for the gateway’s domain. Treat that as an observation of this endpoint, not a rule about proxy ports.
The address printed by the IP-echo endpoint is the address it saw for that request. Check it before adding application headers or moving the request into a program. Related guides cover sending HTTP headers with curl and translating curl requests into Python.
What do you need before starting?
You need a working curl installation, a reachable proxy endpoint and a destination you can test. Gather the proxy scheme, hostname, port, authentication requirements and desired session behavior before troubleshooting.
- Client: record the curl version, operating system and TLS backend.
- Endpoint: confirm which protocol the selected port accepts.
- Authentication: have valid credentials or the required access configuration.
- Destination: begin with an IP-echo endpoint, then test the actual application.
- Configuration: inspect existing proxy variables, bypass rules and .curlrc settings.
Our quick run on October 20, 2026 used an EU Linux server running Ubuntu 24.04, curl 8.5.0, OpenSSL 3.0.13 and nghttp2. We selected a US residential exit and made about 120 requests across syntax, DNS, environment and failure checks. The timing comparison below covers a separate, clearly counted subset of 30 requests.
Keep the initial test small. A successful IP check confirms one route at one moment; it cannot establish whether a different destination will accept your application request.
How do proxy authentication and credentials work?
Use -U or --proxy-user for proxy credentials; -u authenticates to the destination. Proxy and destination authentication are separate, as explained in Everything curl’s proxy authentication chapter.
For the following tested command, first populate PROXY_USER and PROXY_PASS through your local secret-handling process and set GW to the gateway hostname. Double quotes keep the expanded credential pair together as one shell argument.
curl -s -x "http://$GW:823" --proxy-user "$PROXY_USER:$PROXY_PASS" https://api.ipify.org | check "--proxy-user"This line uses the comparison helper shown in the testing section. Quoting addresses shell parsing, not secrecy: command-line credentials can still be exposed. Prefer a protected configuration for repeated use, and never publish raw authentication headers.
| Proxy protocol | Authentication | Compatibility check |
|---|---|---|
| HTTP or HTTPS | Basic by default; other methods include Digest, NTLM and Negotiate | Match the proxy’s advertised method and your curl build. –proxy-anyauth can negotiate a supported method. |
| SOCKS5 or SOCKS5h | SOCKS username/password; GSS-API where supported | HTTP authentication switches do not select SOCKS authentication methods. |
The curl SOCKS5 authentication options distinguish username/password from GSS-API. In our run, a wrong SOCKS5 password produced exit 97 with a user-rejected message, not an HTTP 407 response.
For an HTTP proxy, our wrong-password HTTPS request failed during CONNECT with exit 56 and response 407. The equivalent plain HTTP request returned HTTP 407 with curl exit 0. Checking only the process exit code would have missed that second authentication failure.
How do HTTP versus HTTPS proxies and CONNECT differ?
An HTTP proxy can tunnel an HTTPS destination using CONNECT. An HTTPS proxy additionally encrypts the connection from curl to the proxy itself; the proxy URL and destination URL describe separate connections.
In our run, an HTTPS destination triggered CONNECT to the destination hostname and port 443. After the proxy accepted the tunnel, curl negotiated destination TLS and sent the request inside it. A plain HTTP destination instead used a request containing the full destination URL, without CONNECT.
With an HTTP proxy, the CONNECT exchange and proxy authentication are outside destination TLS. An HTTPS proxy protects that outer exchange too. See Everything curl’s explanation of HTTPS proxies and our HTTP and SOCKS proxy comparison.
Certificate answer: proxy TLS trust and destination TLS trust are separate. Use --proxy-cacert with a trusted certificate bundle for an HTTPS proxy using a private CA or self-signed certificate; --cacert controls destination trust. Confirm the certificate through a trusted channel and check its hostname. Disabling verification creates an impersonation risk, as described in curl’s TLS certificate verification documentation.
Changing a destination to HTTPS does not turn an HTTP proxy endpoint into an HTTPS proxy. Use the scheme that the endpoint actually supports.
SOCKS5 versus SOCKS5h: where does DNS resolve?
socks5:// resolves destination hostnames locally. socks5h:// delegates that resolution to the proxy.
The equivalent flags are --socks5 and --socks5-hostname, respectively. Both the official curl manual and Everything curl’s SOCKS guide document this distinction.
curl -x socks5://USER:[email protected]:824 https://api.ipify.org
curl -x socks5h://USER:[email protected]:824 https://api.ipify.org
Our DNS checks used edns.ip-api.com to observe the resolver handling its hostname. SOCKS5 used our hosting provider’s resolver in France, matching the direct route. SOCKS5h showed US resolvers: T-Mobile USA once and Google LLC twice. HTTPS destinations through the HTTP proxy also showed US resolution because CONNECT carried the destination hostname.
These observations describe the tested configuration, not a fixed resolver assignment. Resolver location also does not prove exit-IP location.
When our local DNS could not resolve a test hostname, SOCKS5 failed locally in about 0.04 seconds. SOCKS5h passed the name onward and failed after about 3.7 seconds when the proxy closed the connection. Moving DNS can change where a failure occurs; it cannot make a nonexistent hostname valid.
For related setups, see DNS over HTTPS and using an SSH SOCKS proxy.
How does curl with proxy handle environment variables, precedence and bypass?
Use lowercase http_proxy for HTTP URLs. A protocol-specific proxy variable takes precedence over ALL_PROXY; the latter is a default, not a retry route after connection failure.
The variable name matches the destination URL scheme. Its value describes the proxy connection. curl’s official environment-variable guide explains case handling, precedence and exclusions.
| Setting tested | Destination | Observed behavior |
|---|---|---|
| http_proxy | HTTP | Proxied |
| HTTP_PROXY | HTTP | Ignored; went direct |
| https_proxy or HTTPS_PROXY | HTTPS | Proxied |
| http_proxy alone | HTTPS | Went direct |
| ALL_PROXY or all_proxy | No matching scheme variable | Used the proxy default |
| Working https_proxy, broken ALL_PROXY | HTTPS | Succeeded through https_proxy |
| Broken https_proxy, working ALL_PROXY | HTTPS | Failed with exit 7 |
| Explicit -x, broken https_proxy | HTTPS | Used -x successfully |
We isolated these checks by unsetting other proxy variables. For bypass, NO_PROXY=api.ipify.org, NO_PROXY=ipify.org and no_proxy=.ipify.org each bypassed the proxy for our test host. A matching NO_PROXY also bypassed an explicit -x.
Use a comma-separated exclusion list for specific hosts and --noproxy '*' to bypass all proxies for a request. To override an inherited exclusion list and force the selected proxy, use an empty --noproxy value. The manual’s bypass reference specifies this behavior.
How do you persist settings with .curlrc?
Use .curlrc for defaults you intentionally want curl to load across commands. A separate configuration selected with --config is easier to scope to one task.
For example, a configuration can contain proxy = "http://gw.dataimpulse.com:823" and a separate proxy-user = "USER:PASS" entry, one per line. Replace the markers privately, restrict the configuration to its owner, and exclude it from version control and shared archives.
These are configuration syntax examples, not additional measured tests. The official configuration guide documents long option names, quoted values and automatic loading.
Persistent settings can explain why a command behaves differently across machines. Check them alongside environment variables and bypass lists. To skip automatic configuration loading during diagnosis, put -q first after curl, as specified by the configuration-disable option.
A saved proxy setting does not guarantee every request uses that proxy: later options and bypass rules still matter. Keep credentials out of screenshots even when the configuration itself has restricted access.
How do you test connectivity and troubleshoot errors?
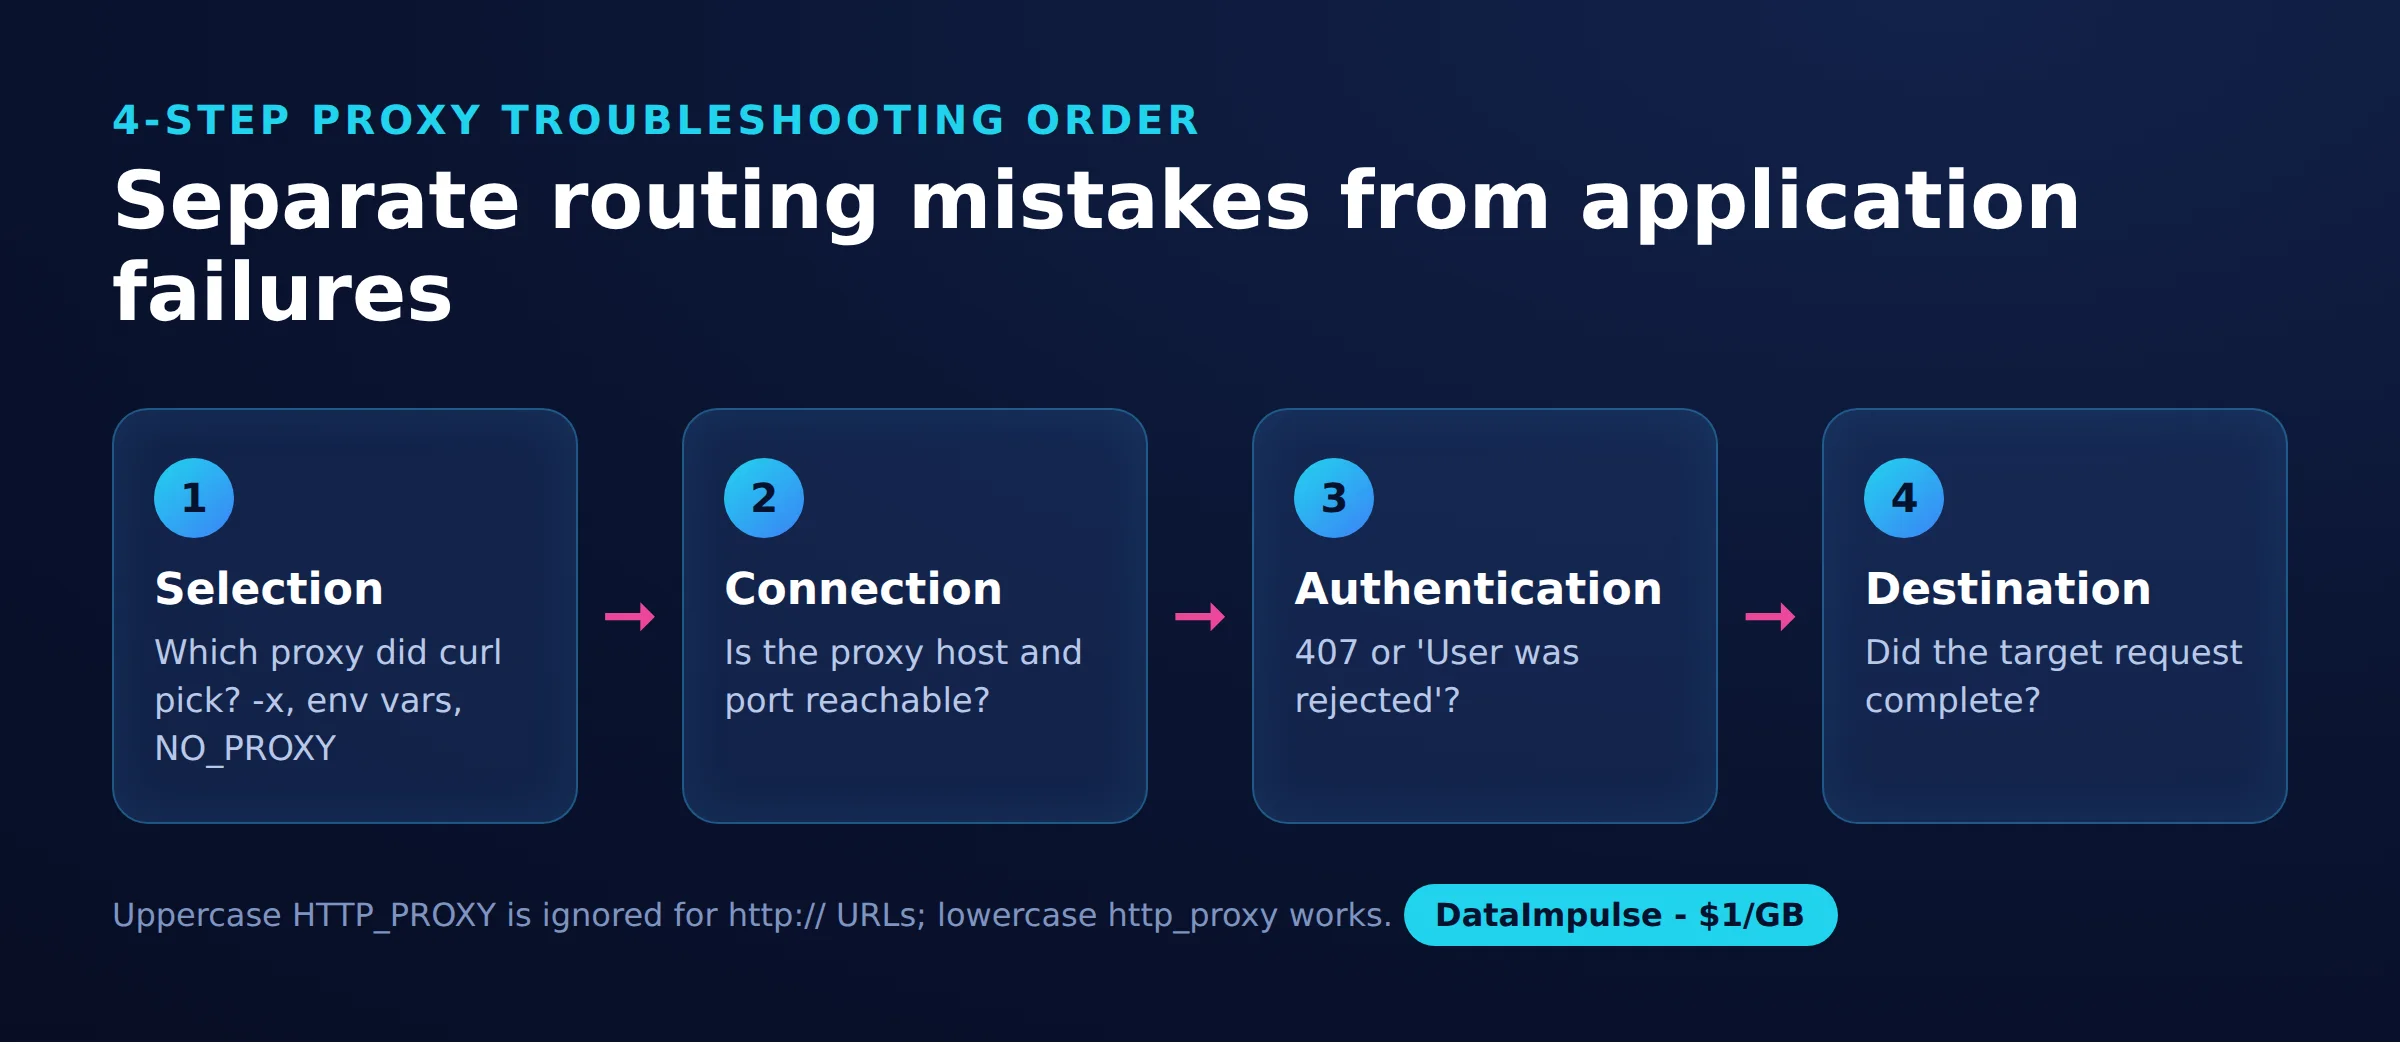
Compare direct and proxied responses from the same IP-echo endpoint, then inspect HTTP status and curl’s exit code. Use the 4-layer Proxy Check: selection, connection, authentication and destination.
Check which proxy was selected, whether its hostname and port are reachable, whether authentication succeeded, and finally whether the destination request completed. This order separates routing mistakes from application failures.
The following excerpt establishes a direct baseline and compares a proxied response. Set PROXY_USER and PROXY_PASS privately before running it.
GW=gw.dataimpulse.com
P="http://$PROXY_USER:$PROXY_PASS@$GW:823"
MY_IP=$(curl -s --noproxy '*' https://api.ipify.org)          # our own IP, for comparison
check() { ip=$(cat); [ "$ip" = "$MY_IP" ] && echo "direct  <- $1" || echo "proxied <- $1"; }
clean() { env -u http_proxy -u HTTP_PROXY -u https_proxy -u HTTPS_PROXY -u ALL_PROXY -u all_proxy -u NO_PROXY -u no_proxy "$@"; }
curl -s -x "http://$GW:823" --proxy-user "$PROXY_USER:$PROXY_PASS" https://api.ipify.org | check "--proxy-user"Helper limit: this comparison labels any different text as proxied, including an empty or error response. Accept the result only after confirming a valid IP response and successful HTTP status. Our measurements checked response validity separately.
For a narrow view of CONNECT, this tested filter retains the CONNECT request and first HTTP response line:
curl -sv -x "$P" https://api.ipify.org -o /dev/null 2>&1 | grep -E '^> CONNECT|^< HTTP/1.1' | head -2Inspect even filtered output before sharing it. Our unfiltered verbose log included Proxy-Authorization with a Basic credential value. Base64 is not encryption; remove that header, destination authorization, cookies and other secrets from diagnostic logs.
| Symptom in our run | Check | Fix or next step |
|---|---|---|
| Exit 5: could not resolve proxy | Gateway spelling and local DNS | Correct the hostname before testing authentication. |
| Exit 28 on port 8123 | Port, reachability and firewall | Use the configured port. Our 15-second timeout expired; there was no immediate refusal. |
| Exit 56, CONNECT response 407 | Missing or incorrect HTTP proxy credentials | Correct proxy authentication. |
| Exit 0, HTTP 407 | Plain HTTP response status | Treat the response as authentication failure despite the zero exit code. |
| Exit 97, SOCKS user rejected | SOCKS credentials | Correct the login before repeating the DNS test. |
| Exit 97, local hostname resolution failure | Destination DNS with socks5:// | Fix local DNS or select proxy-side resolution when appropriate. |
| Exit 97 with socks4a:// | Endpoint protocol compatibility | Use an accepted protocol; this gateway rejected SOCKS4 in our run. |
The direct times are our server calling the API with no proxy hop at all; the proxied times include an extra route through a residential connection, so the difference shows the cost of that hop in a small sample, not a ranking of providers or a benchmark.
Our quick run on October 20, 2026: we sent 10 requests per mode to https://api.ipify.org, one second apart, with a new connection each time. The direct route, rotating port 823 and sticky session used the same client and target.
| Mode | Successful requests | Failures | Distinct observed IPs | Median total time |
|---|---|---|---|---|
| Direct | 10/10 | 0/10 | 1 | 156 ms |
| Rotating | 10/10 | 0/10 | 10 | 892 ms |
| Sticky | 10/10 | 0/10 | 1 | 859 ms |
Source: our quick run on October 20, 2026, including the curl_proxy_examples.sh test script and recorded observations. This is a small snapshot, not a benchmark. The 30-request comparison had no failures; intentionally induced failures belong to the broader checks. We used external IP-echo services, not an endpoint under our control, and these results do not predict other destinations or workloads.
If the tunnel succeeds but the destination rejects the request, investigate the application response separately. Our guide to HTTP 403 responses covers that next stage.
How do DataImpulse setup, rotation and sticky sessions work?
Configure the gateway, credentials, country selection and session mode, then verify the resulting exit IP. Rotation and stickiness depend on provider configuration and address availability.
DataImpulse offers residential proxies from $1 per GB, with country targeting included across 195 countries, plus datacenter and mobile proxies.
Our test used the residential gateway with a US exit. Rotating mode produced 10 different IPs in 10 requests, while the sticky configuration retained one IP across its 10 requests. Neither observation guarantees the next request’s IP, a fixed session duration or uninterrupted address availability.
| Choice | Use when… | Avoid when… |
|---|---|---|
| Rotating sessions | Use rotating sessions when independent requests can tolerate changing exit IPs. | Avoid rotating sessions when a workflow depends on keeping one address. |
| Sticky sessions | Use sticky sessions when related requests benefit from address continuity. | Avoid treating sticky sessions as permanent or static address ownership. |
| Per-request proxy settings | Use -x when debugging or choosing a route explicitly. | Avoid assuming -x defeats an existing bypass rule. |
| Persistent settings | Use a configuration when repeated commands should share deliberate defaults. | Avoid broad defaults when unrelated tasks need different routes. |
Rotation does not remove rate limits or guarantee destination acceptance. Start with the session behavior your workflow needs, then measure valid responses, failures and timing against your actual target.
Frequently Asked Questions
What is the simplest way to use curl with proxy?
Select the endpoint with -x, then specify the destination URL separately. If authentication is required, use -U or –proxy-user. Start with an IP-echo request so you can inspect the route before testing a larger workflow.
Why does uppercase HTTP_PROXY not work?
curl deliberately ignores HTTP_PROXY; use lowercase http_proxy for HTTP destinations. HTTPS_PROXY is accepted for HTTPS destinations. Our isolated variable checks reproduced both behaviors.
Should I choose SOCKS5 or SOCKS5h?
Choose based on where destination DNS should happen. SOCKS5 uses local resolution, while SOCKS5h asks the proxy to resolve the destination. Our resolver checks showed different resolver locations for those two settings.
Does an HTTPS destination require an HTTPS proxy?
No. Our HTTP proxy successfully established a CONNECT tunnel for an HTTPS destination. Selecting an HTTPS proxy adds encryption to the client-to-proxy connection as well.
How should I handle a self-signed HTTPS proxy certificate?
Obtain and verify the appropriate trust certificate through a trusted channel, then select it with –proxy-cacert. Destination certificate trust uses a separate setting. Do not treat disabling verification as a permanent repair.
Can curl exit successfully even when proxy authentication fails?
Yes: our plain HTTP wrong-password test returned exit 0 alongside HTTP 407. Check the response status as well as the exit code. The HTTPS version failed during CONNECT instead.
Will a rotating proxy return a new IP every time?
Our 10-request rotating sample returned 10 distinct IPs, but that is only one small observation. Subsequent assignments depend on configuration and availability. Verify actual responses instead of assuming every request changes address.
Does a sticky session mean a static residential IP?
No. Our sticky sample kept one address for 10 requests, which demonstrates continuity only during that sample. It does not establish permanent ownership or guarantee future availability.
Test one route before scaling
If you need a residential exit for your curl workflow, DataImpulse offers residential traffic from $1 per GB with country targeting included. Start with a small IP check, choose rotating or sticky behavior deliberately, and measure results against your own destination before committing more traffic.
Last updated: October 20, 2026.

 State/City/Zip/ASN Targeting




