
In this Article
HTTP 302 is a temporary redirect, not inherently an error. An HTTP 302 response normally points to another URL in the Location header; inspect that destination and the redirect chain before changing anything. Unexpected login pages, loops, or changed POST requests require different actions. First determine whether the application, CDN, or client behavior explains the result. RFC 9110 defines 302 semantics.
Record the destination, method, and returned content before changing redirect rules or adding retries.
Key Facts
- 302 Found identifies a temporary redirect. RFC 9110: 302 Found.
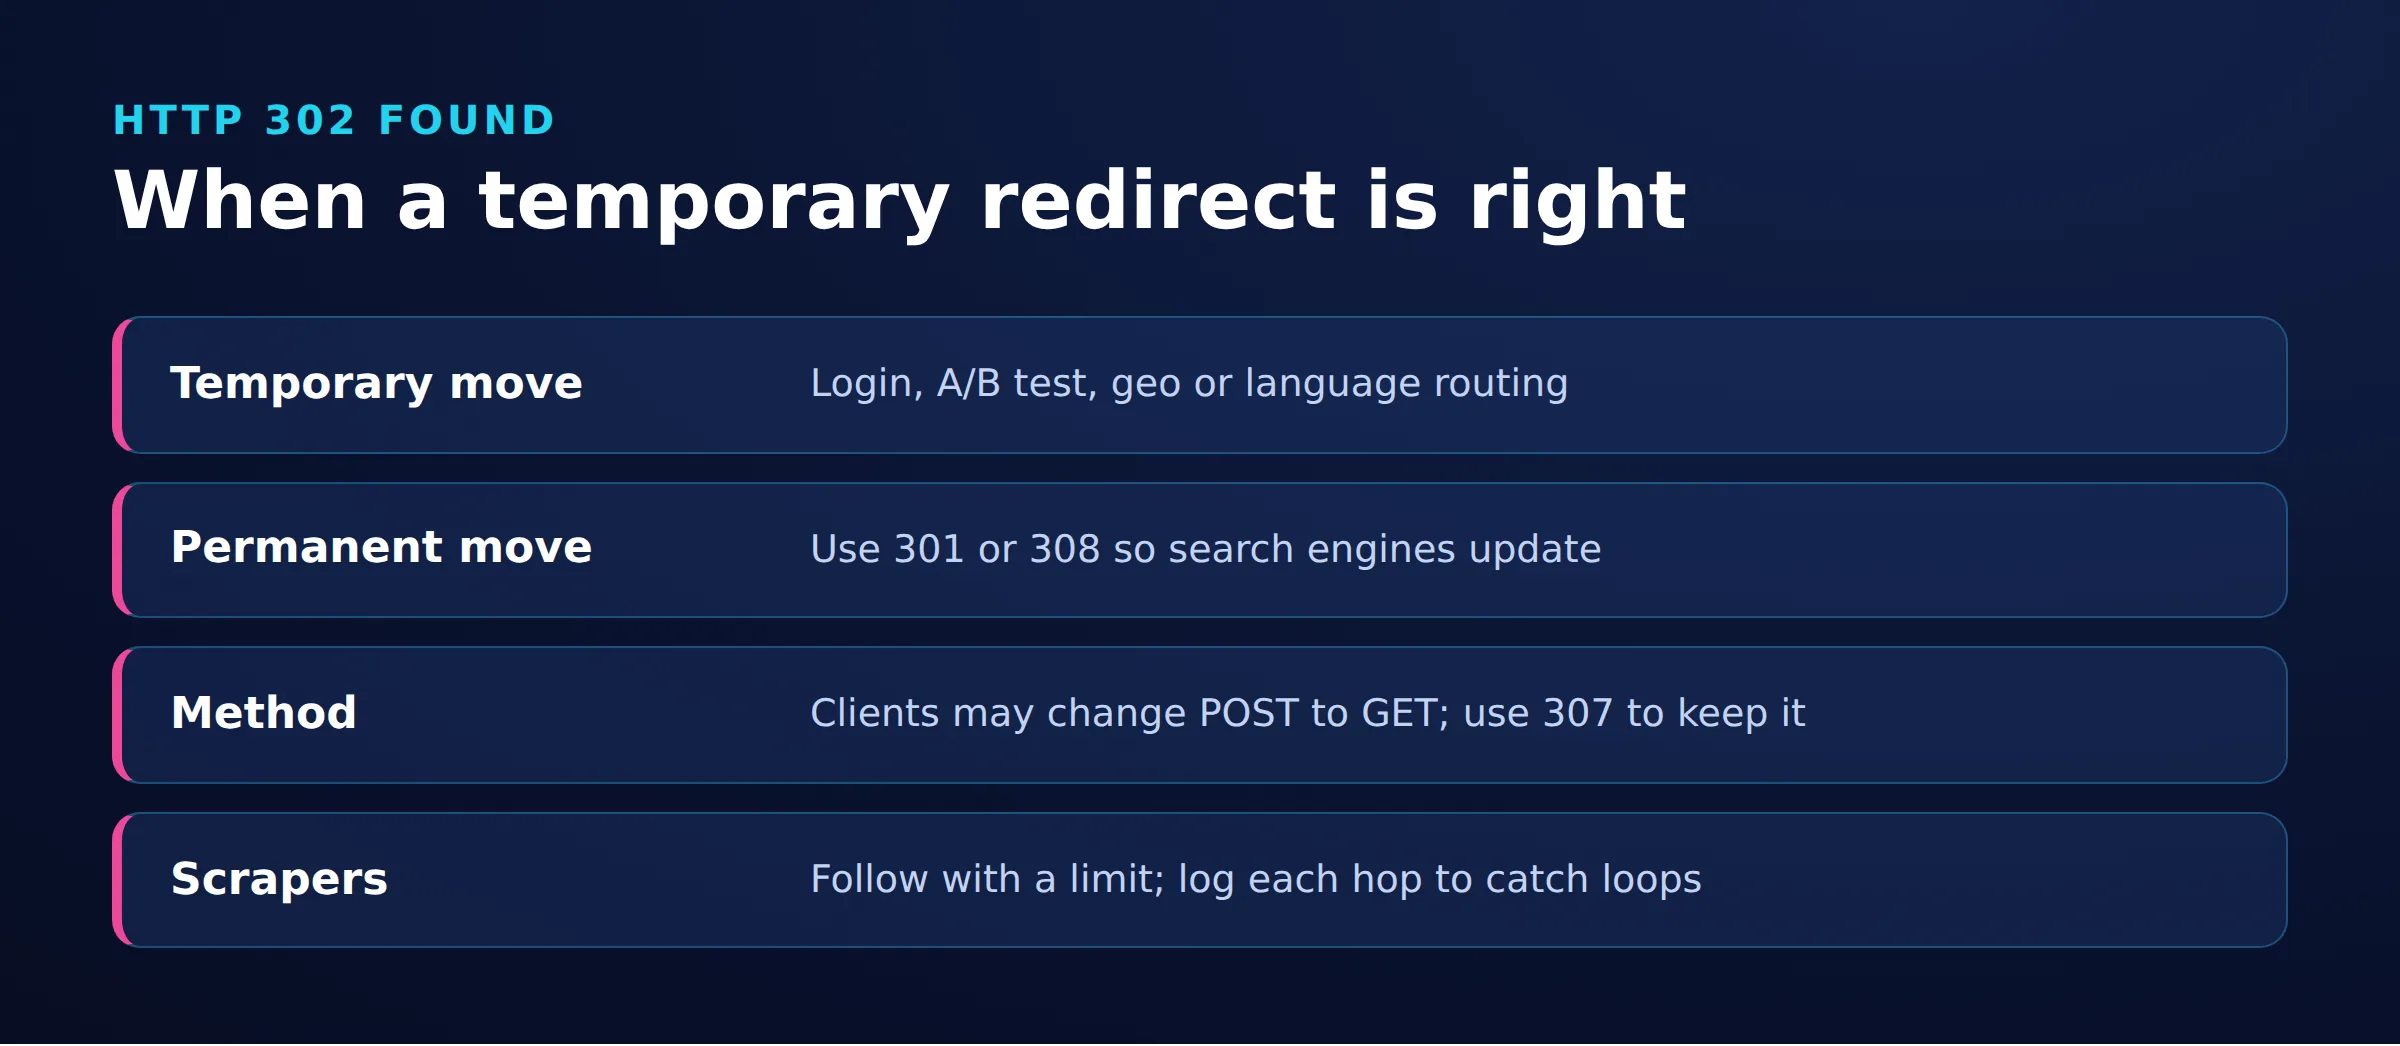
Locationcan contain a relative URL. RFC 9110: Location.- A client may change
POSTtoGETafter 302. RFC 9110: 302 Found. - 307 forbids changing the method during automatic redirection. RFC 9110: 307 Temporary Redirect.
- A final 200 response does not establish that the expected content arrived; validate the content as well as the status.
What HTTP 302 Found means, and why you see it instead of 200
302 is a response status, not a request type. It directs the client elsewhere temporarily; the original URL remains relevant for future requests. Read the protocol definition.
Found is not Not Found. For surrounding codes, see the HTTP status-code hub.
Inspect the raw response and Location header
Run these commands in Bash with an absolute HTTP or HTTPS URL. The first request displays the response without following redirects. The second follows up to five redirects and prints the final URL and HTTP status.
read -r -p 'Target URL: ' TARGET_URL
curl -i --max-time 20 "$TARGET_URL"
curl -i -L --max-redirs 5 --max-time 20 \
  --write-out '\nFinal URL: %{url_effective}\nStatus: %{http_code}\n' \
  "$TARGET_URL"
The --max-redirs 5 option limits following to five redirects. See the redirect-limit documentation and inspecting headers with curl.
These curl commands do not reproduce an authenticated browser session. For a route that sets cookies during redirection, add --cookie "" to the second command to enable cookie handling within that invocation. This starts without existing cookies; it does not log you in or import your browser session. Compare requests with equivalent authorized session state before attributing a difference to server rules. Cookie handling.
With https://httpbin.org/redirect-to?url=/get&status_code=302, the response and final-result excerpts are:
HTTP/2 302
location: /get
Final URL: https://httpbin.org/get
Status: 200A relative Location such as /get resolves against the requested URL. RFC Location rules.
Unexpected HTTP 302: find the responsible layer
Identify which layer issued the redirect. Correlate timestamps and request identifiers with application, origin, and CDN logs; compare the incoming URL, scheme, session state, outgoing status, and Location.
| Symptom | Check | Meaning | Fix/action |
|---|---|---|---|
| Crawl-time 302 | Destination, chain, final content | Redirect encountered; not necessarily failure | Accept intended route or correct destination |
| Login page replaces data | Cookies, session, Location |
Possible authentication flow | Restore authorized session/API route |
| Repeated URLs | Full chain; origin/CDN scheme rules | Possible conflicting redirects | Correct rule at responsible layer |
POST becomes GET |
Destination method/body | 302 permits method change | Server owner: return 307 when temporary redirection must preserve the method. |
| Country changes | Equivalent initial session/headers; vary egress | Possible geo-routing | Use intended region and stable egress |
| Client stops at 302 | Follow settings; missing Location |
Client policy or incomplete response | Enable appropriate following or repair response |
For example, Cloudflare Flexible mode connects to the origin over HTTP. If the origin redirects those requests to HTTPS, the combination can produce a loop. Confirm the encryption mode and origin logs, then align the configuration; Full or Full (strict) requires HTTPS support at the origin. Cloudflare loop diagnosis.
For regional comparisons, a changed result is a clue, not proof that IP location alone caused it. See country-dependent results.
407 requests proxy authentication, while 302 redirects. RFC 407 definition. Use the 407 troubleshooting guide for that branch.
What to do by role
| Role | Next action |
|---|---|
| Visitor | Report the loop and affected URL. |
| Developer | Compare destination method, body, and session state. |
| Server owner | Audit redirect rules against origin/CDN logs. |
| Scraper/API operator | Record every hop and validate content. |
Python Requests
This script requires Python 3, the Requests package, and an absolute HTTP or HTTPS URL. allow_redirects=False disables following; the timeout is not a total download deadline. Requests quickstart.
import requests

def log_response(response, *args, **kwargs):
    print(
        response.request.method,
        response.status_code,
        response.url,
        "Location:", response.headers.get("Location"),
    )

url = input("Target URL: ").strip()

with requests.Session() as session:
    session.max_redirects = 5
    session.hooks["response"].append(log_response)

    try:
        first = session.get(
            url, allow_redirects=False, timeout=10
        )
        answer = input(
            "Start a new GET and follow a trusted route? [y/N] "
        )
        if answer.strip().lower() == "y":
            response = session.get(url, timeout=10)
            print("Redirect responses:", len(response.history))
            print("Final URL:", response.url)
            print("Content-Type:",
                  response.headers.get("Content-Type"))
    except requests.TooManyRedirects:
        print("Stopped: redirect limit exceeded; inspect hops above.")
    except requests.RequestException as exc:
        print(f"Request failed: {exc}")
Each response is logged as it arrives, including responses before the redirect limit is exceeded. The second request restarts the original URL and retains cookies set by the first response; its route can therefore differ. For controlled comparisons, reproduce the same initial authorized session state. See response hooks, session persistence, and the redirect limit.
For adapting requests, see curl to Python. Never blindly forward credentials across hosts.
Diagnose changed POST requests
With curl, -L --data 'probe=1' sends an initial POST; following a 302 normally changes the next request to GET. Inspect the destination’s recorded method and body. Avoid -X POST because it overrides method selection. Redirect behavior. If temporary redirection must preserve the method, use 307.
C# HttpClient
Place this example in Program.cs in a console application supporting C# 9 or later. It displays only the initial response status and Location header. Top-level statements.
using System;
using System.Net.Http;

using var handler = new HttpClientHandler { AllowAutoRedirect = false };
using var client = new HttpClient(handler);
client.Timeout = TimeSpan.FromSeconds(10);
Console.Write("Target URL: ");
using var response = await client.GetAsync(Console.ReadLine()!);
Console.WriteLine((int)response.StatusCode);
Console.WriteLine(response.Headers.Location);
During automatic redirects, Authorization is cleared and reauthentication is attempted. .NET Core and .NET 5+ do not automatically follow HTTPS-to-HTTP redirects. Microsoft redirect behavior.
Got an HTTP 302 response at crawl time?
Record the starting URL, each destination, final status, content type, time, and client settings. Check whether the chain ended at the intended page, a login form, or another failure.
For Wayback Machine messages, retain the exact archived URL and message. For Java RedirectionException or unsuccessful webhooks, inspect the response and receiver contract before changing redirect handling.
HTTP 302 vs 301, 307, and 308
Choose by permanence and method requirements.
| Code | Duration | Method on following |
|---|---|---|
| 301 | Permanent | POST may become GET |
| 302 | Temporary | POST may become GET |
| 307 | Temporary | Must preserve method |
| 308 | Permanent | Must preserve method |
RFC redirect definitions. Use 303 See Other when a POST should lead to retrieval of a separate result resource with GET.
Does 302 pass link equity?
Canonical selection and PageRank are different questions. Google documents permanent redirects as a signal favoring the destination as canonical. Temporary redirects do not supply that signal, although other signals can still lead to destination indexing. Google’s redirect guidance.
That guidance does not establish a fixed link-equity percentage or guarantee indexing. Choose the status that reflects the actual move.
Follow, retry, or leave it alone?
Follow an intended, trusted destination; repair an incorrect rule; leave a working temporary redirect alone.
Verify the final URL, content, destination method/body, and absence of loops. A login page returning 200 still fails a data-retrieval requirement. Diagnose before configuring Requests retries, especially for operations with side effects.
Frequently Asked Questions
Is HTTP 302 an error?
It identifies temporary redirection. Investigate when the destination or behavior conflicts with the request’s purpose.
Why am I seeing 302 instead of my data?
Inspect Location. If it leads to login, check your authorized session and intended API route.
What should a crawl-time 302 report contain?
Include the starting URL, each destination, final status, content type, time, and client settings.
How should I investigate a redirect loop?
Record repeating URLs and compare those hops with application and infrastructure rules.
Should every 302 become a 301?
No. Establish whether the move is permanent before changing its meaning.
Can changing proxies fix a 302?
Egress changes can investigate regional routing. They cannot repair server rules or replace an authorized session.
Compare egress only when routing is the question
DataImpulse proxies can provide egress points for controlled regional comparisons. Start each comparison with equivalent request headers and authorized session state, and keep the chosen egress stable during each chain. Let the client apply cookie scope and redirect authentication rules; do not copy credentials to another host. See Requests session behavior and Microsoft redirect authentication behavior.
Last updated: November 18, 2026.

 State/City/Zip/ASN Targeting




