
In this Article
Cloudflare error 1015 means a website’s rate limiting rule has temporarily restricted your requests. To resolve error 1015, pause requests, follow Retry-After when provided, and contact the site owner if access remains blocked. Owners should inspect the matching rule; automated clients should reduce request volume. Shared VPN or proxy addresses can contribute when limits count requests by IP.
Start by identifying your role and saving the failed response. Cloudflare documents owner-configured request limits (as of November 2026) and recommends waiting or contacting website support. See its 1015 troubleshooting guidance. The shared-address explanation is conditional: verify how requests are counted before blaming the network.
Key Facts
- Stop duplicate requests before investigating a rate limit.
- Record the affected URL, timestamp, timezone and displayed Ray ID.
- Treat shared-IP interference as a hypothesis until the owner checks the rule.
- A retry delay is not a guarantee that the next request will succeed.
- Bound automated retries and escalate when the attempt budget is exhausted.
- Our November 17, 2026 local fixture snapshot covered seven retry scenarios with the revised helper, not real Cloudflare enforcement.
Confirm the symptom and who controls it
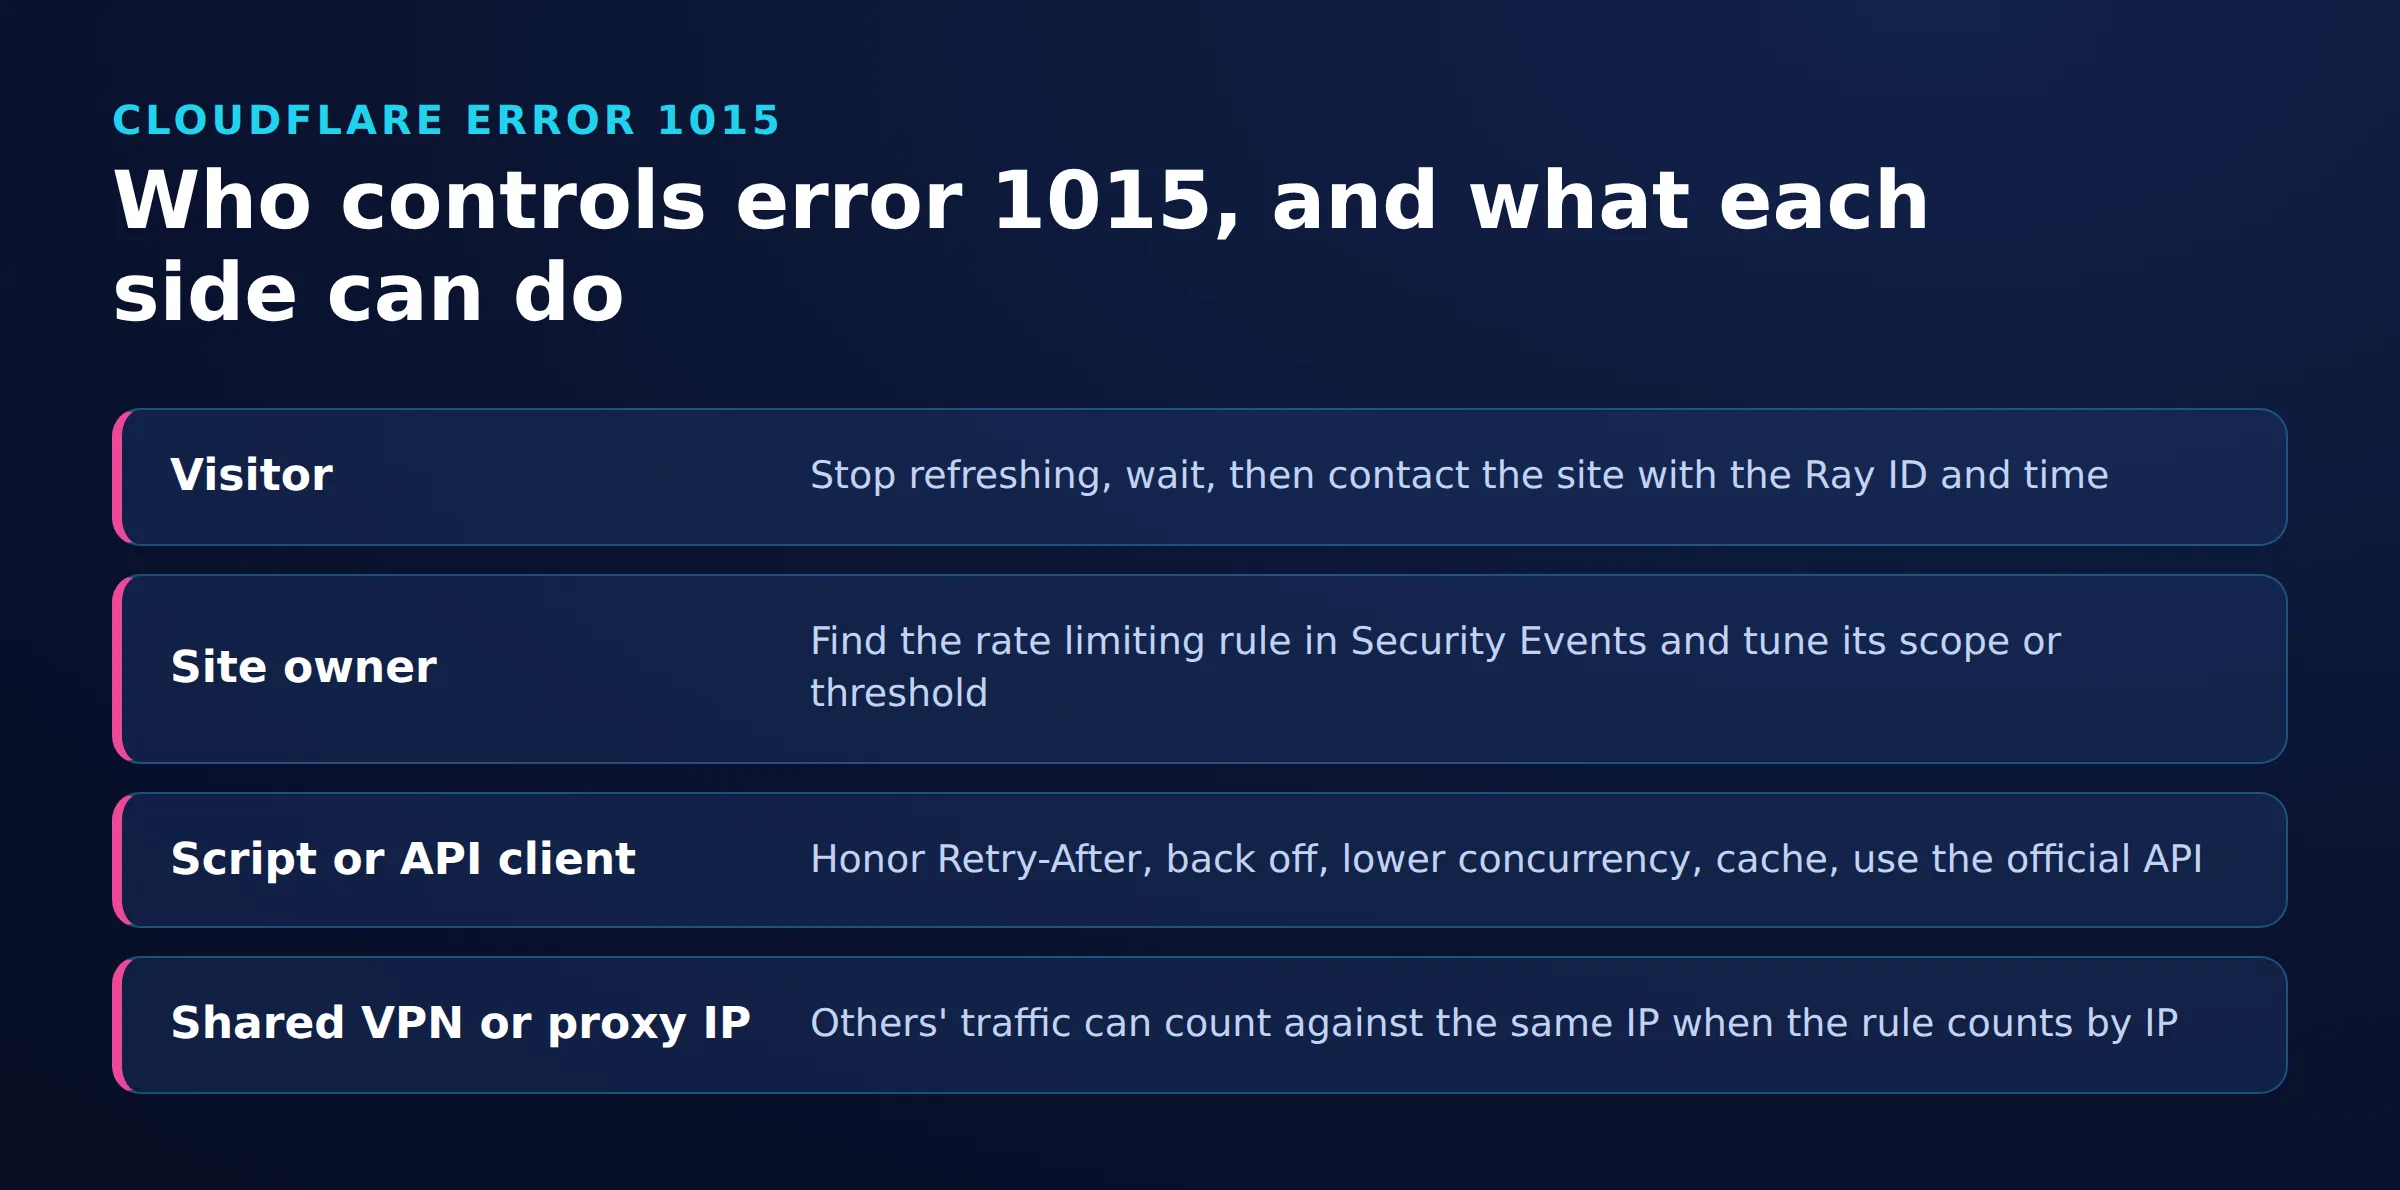
Confirm that the page explicitly identifies Cloudflare and says 1015 or You are being rate limited. The website owner sets the policy, Cloudflare enforces it, and your browser or client generates the requests.
| Role | What you control | Next action |
|---|---|---|
| Visitor | Your browsing activity | Stop duplicate requests, wait, then contact website support if necessary. |
| Site owner | The website’s rate-limit policy | Find the matching rule, adjust narrowly and validate. |
| Authorized client developer | Request volume and retry behavior | Honor Retry-After, reduce concurrency and stop when retries are exhausted. |
Keep the page identifier separate from the HTTP response status. Cloudflare’s default rate-limit error page displays 1015 with HTTP 429 unless custom error handling changes the response (as of November 2026). See Cloudflare’s error-page troubleshooting.
HTTP 429 means too many requests within a period, according to RFC 6585, section 4. It does not, by itself, identify the enforcing service. Record both the status and page text; our HTTP status code guide explains the distinction.
For a shared VPN or proxy connection, ask the owner whether affected requests share a counting key. Treat that as an investigation, not proof that another user caused your interruption.
Diagnose error 1015 before changing anything
Collect evidence before changing browsers, networks or client settings. The patterns below suggest what to investigate; they do not establish the cause.
| Symptom | Check | Meaning | Fix |
|---|---|---|---|
| After repeated clicks or refreshes | Tabs, extensions, request timestamps | Client bursts may trigger policy | Stop duplicates; pause |
| On shared VPN/proxy | Owner’s counting characteristic and logs | IP-based counting may aggregate users | Pause; request owner review |
| Legitimate users blocked | Matching rule, scope, threshold, period | Policy may be too broad or strict | Tune the specific rule |
| Script repeatedly blocked | Headers, concurrency, retry logs | Traffic or retry amplification | Backoff, reduce concurrency, cache |
| Still blocked after waiting | Retry-After, Ray ID, timestamp | Duration or recurring trigger remains uncertain | Escalate with evidence |
Save the URL, method, response status, relevant headers and time with timezone. Redact cookies, authorization headers and sensitive query parameters before sharing diagnostics.
For shared-egress investigations, record the connection used when the failure occurred. Our rotating versus static proxy guide offers background; changing addresses should not become a strategy for exceeding the website’s limits.
What should visitors do, including on US visa scheduling websites?
Stop refreshing, pause auto-refresh tools and preserve the current session while you gather details. If access remains blocked, contact the website’s support team with the evidence already collected.
US visa scheduling, USTravelDocs and VFS Global
Apply this workflow only when the affected page explicitly shows Cloudflare 1015. A booking failure or another numbered error needs its own diagnosis.
Keep a screenshot and note the action immediately before the interruption: opening the calendar, signing in or submitting a form. Avoid repeated submissions. Ask support to confirm the transaction or appointment state before repeating an action with consequences.
Do not assume a booking-specific cooldown from the error number. Use instructions from the affected website’s official support channel, including any guidance about preserving or restarting the session.
AMC, GameStop, PayPal and other websites
For AMC, GameStop, PayPal, Stake, VSCO, Notion, hosting, gaming, streaming or email services, apply this workflow only when the response explicitly identifies Cloudflare error 1015. For Apple, Airalo or other apps, a numeric error alone is insufficient; confirm the Cloudflare message before using these steps.
Why cookies, browsers and VPN switching are not universal fixes
If the counter groups requests by IP, changing local browser state does not change that counting key. This is an inference from IP-based counting, not a diagnosis of your session. Avoid deleting session data or switching VPN endpoints as an automatic response. Ask support which change, if any, addresses the observed cause.
How should site owners fix legitimate traffic being blocked?
Locate the matching event and rule before changing protection settings. Adjust the smallest relevant part of the policy, then validate the affected user journey.
Cloudflare supports Ray ID filtering in Security Events, but sampled results can omit requests (as of November 2026). Narrow the time range; an absent result does not prove the request escaped enforcement. See the Ray ID documentation.
Inspect scope, counting characteristics, counting expression, threshold, period and mitigation duration. Cloudflare documents these configurable rate-limit parameters (as of November 2026) in its parameter reference. When IP is the relevant grouping characteristic, users sharing that address may contribute to the same counter; that conclusion depends on the complete rule.
- Compare the blocked action with the intended protected endpoint.
- Check whether legitimate page activity creates more requests than the policy anticipates.
- Review whether the threshold and counting period match the intended workload.
- Make a narrow change and retain the previous settings for rollback.
For broader design questions, see our API rate limiting guide. Document why the adjustment is justified, then compare successful traffic and unwanted traffic after the change.
How should scrapers and API clients recover?
Pause the affected workload, reduce concurrency and coordinate retries across workers. Use an official API where available, deduplicate requests, cache reusable results and ask the owner about an approved allowance or narrowly scoped allowlist.
Retry-After accepts either delay-seconds or an HTTP-date under RFC 9110, section 10.2.3. The helper below retries GET responses with 429 or 503, bounds attempts and uses capped exponential backoff with full jitter when the header is absent or invalid. It treats timezone-free asctime HTTP-dates as UTC, as required by RFC 9110, section 5.6.7.
Server-directed waits are honored in full. If the delay exceeds the job’s available time, stop and defer the job. Set max_wait to the maximum individual delay your job can accept; the default is 300 seconds. A longer delay stops the helper without retrying early. The cap applies only to fallback backoff, not Retry-After.
The exhaustion message reports the last HTTP status because 503 can indicate temporary overload or maintenance rather than rate limiting. See RFC 9110, section 15.6.4.
import random, time
from email.utils import parsedate_to_datetime
from datetime import datetime, timezone
import requests

def retry_after_seconds(value):
    """Return the wait in seconds from a Retry-After header, or None if absent/invalid."""
    if not value:
        return None
    value = value.strip()
    if value.isdigit():
        return int(value)
    try:
        when = parsedate_to_datetime(value)
    except (TypeError, ValueError):
        return None
    if when.tzinfo is None:  # asctime HTTP-dates carry no zone; RFC 9110 dates are GMT
        when = when.replace(tzinfo=timezone.utc)
    return max(0.0, (when - datetime.now(timezone.utc)).total_seconds())

def polite_get(url, max_attempts=4, base=2.0, cap=60.0, max_wait=300, timeout=15):
    """GET with bounded retries on 429/503.
    Honors Retry-After in full; without it, uses capped exponential backoff with full jitter.
    Stops (instead of waiting) if the server asks for more than max_wait seconds."""
    if max_attempts < 1:
        raise ValueError("max_attempts must be at least 1")
    for attempt in range(1, max_attempts + 1):
        resp = requests.get(url, timeout=timeout)
        if resp.status_code not in (429, 503):
            return resp
        wait = retry_after_seconds(resp.headers.get("Retry-After"))
        if wait is None:
            wait = random.uniform(0, min(cap, base * 2 ** attempt))
        if wait > max_wait:
            raise RuntimeError(f"server asked to wait {wait:.0f}s (over max_wait); "
                               "stop and reschedule the job")
        if attempt == max_attempts:
            break
        print(f"attempt {attempt}: HTTP {resp.status_code}, "
              f"Retry-After={resp.headers.get('Retry-After')!r}, sleeping {wait:.1f}s")
        time.sleep(wait)
    raise RuntimeError(f"retry budget exhausted after {attempt} attempt(s); "
                       f"last HTTP status {resp.status_code}; stop and escalate")
Our November 17, 2026, 16:37 UTC snapshot used Python 3.12.3 and requests 2.34.2 with this revised helper against a local HTTP fixture returning 429 with a Cloudflare-style 1015 body. We ran the seven scenarios below. This was a local imitation, not real Cloudflare enforcement, and is not a benchmark.
| Fixture scenario | Observed result |
|---|---|
| Retry-After: 2; first two requests return 429 | Two 2.0-second waits; HTTP 200 after 4.0 seconds |
| Retry-After: Tue, 17 Nov 2026 16:38:01 GMT; first request returns 429 | One 2.2-second wait; HTTP 200 after 2.2 seconds |
| Retry-After: Tue Nov 17 16:38:04 2026 (asctime); first request returns 429 | One 2.2-second wait; HTTP 200 after 2.2 seconds |
| Retry-After: soon (malformed); first two requests return 429 | Fallback waits logged as 2.3 and 1.5 seconds; HTTP 200 after 3.9 seconds |
| No Retry-After header; first two requests return 429 | Fallback waits logged as 3.8 and 5.0 seconds; HTTP 200 after 8.8 seconds |
| Retry-After: 3600; first request returns 429 | server asked to wait 3600s (over max_wait); stop and reschedule the job (0.0s) |
| Retry-After: 2; fixture configured to return 429 for the first nine requests | Three 2.0-second waits; retry budget exhausted after 4 attempt(s); last HTTP status 429; stop and escalate (6.0s) |
The snapshot does not cover 503 or network exceptions. Network exceptions escape the helper; other statuses return for caller inspection. Do not wrap failures in an unlimited restart loop. See our Python requests retry guide for integration context.
For authorized proxy configurations, consider session continuity separately from request budgets. Proxy selection cannot grant permission to exceed a website’s policy.
How long does error 1015 last?
There is no universal waiting period or guaranteed countdown. Use the response’s retry guidance and the owner’s instructions instead of assuming every interruption lasts minutes or hours.
Cloudflare documents a default 1015 Retry-After value of 30 seconds, with a dynamic WAF rate-limit value taking precedence (as of November 2026). See its error-response reference. That is guidance for when to retry, not proof that every block expires after 30 seconds.
Keep the counting period, mitigation duration and retry delay conceptually separate. The first describes the observation window, the second the enforcement interval, and the third when the client should next try. If the header is absent, pause and seek owner guidance rather than inventing a precise expiry time.
How do you verify recovery and recognize a different error?
After waiting, make one controlled request and confirm that it returns the expected page or API content. Owners should also inspect corresponding events before restoring the full workload.
- HTTP 429: investigate the rate limit and its enforcing layer.
- HTTP 403: the server understood the request but refuses it, as defined in RFC 9110. Follow the separate 403 diagnosis guide.
- A challenge page: follow its displayed instructions; do not classify it as 1015 without that message.
- A suspected permanent ban: ask the website owner to confirm the policy. Repeated failures alone do not establish permanence.
If the controlled request fails, save the new timestamp and response details, stop again and escalate. If it succeeds, resume conservatively while monitoring for recurrence.
Frequently Asked Questions
Can I remove error 1015 myself?
You can stop duplicate traffic and wait before checking again. If the interruption persists, send the website’s support team your URL, timestamp and error details.
Does error 1015 mean my account is permanently banned?
Do not infer an account ban from this message alone. Ask the owner to distinguish the request restriction from any separate account policy.
Should I switch my VPN server?
Do not use address switching to work around the limit. First ask whether shared-address counting explains the failure and what connection the owner approves.
What should I send support for a visa scheduling interruption?
Send the affected URL, time and timezone, screenshot and displayed Ray ID. Describe the last action and ask support to confirm its outcome before submitting again.
Should I clear cookies?
Avoid making that your first troubleshooting step. Preserve the session and ask support whether a session reset addresses the diagnosed cause.
What if Retry-After is missing?
Do not interpret a missing header as permission to retry immediately. Automated clients should use bounded backoff; visitors should pause and seek guidance if access remains blocked.
Does the Python example prove recovery from Cloudflare?
No. The seven-scenario snapshot exercised the revised helper against a local imitation of a rate-limit response, so it cannot establish recovery times or success rates on a live website.
How long does error 1015 last?
There is no universal duration. Cloudflare documents a default Retry-After of 30 seconds, but a dynamic WAF value takes precedence; neither guarantees recovery. See Cloudflare’s error-response reference.
Build a recovery path that respects the limit
Save the evidence, identify who controls the policy and make one controlled recovery check. For recurring failures, agree on a request budget and escalation path with the website owner before resuming the workload.
Last updated: November 17, 2026.

 State/City/Zip/ASN Targeting




